

Our healthcare compliance services run end to end, from a device facing the FDA to patient data inside a hospital. Bring us in at any stage.
Gesundheitswesen Compliance Dienstleistungen

15+
Jahre im Gesundheitswesen
150+
Experts in healthcare
25+
FDA- und CE-Zulassungen
93%
CSAT across client projects
100%
Compliance-erste Architektur
Our healthcare compliance services
You can take the whole program, or take the single piece your team is missing right now.
Regulatorische Wege für Medizinprodukte und SaMD
We take a device, or a piece of software that counts as one, from early strategy through to a submission that holds together under review. For regulated products, the work starts with intended use, regulatory status and classification, followed by selection of the applicable pathway and evidence strategy.
- Device classification and submission pathway selection
- Predicate analysis for a 510(k), De Novo, or PMA route
- EU MDR technical file and clinical evaluation support
- Design and development file support and regulatory submission documentation
- Alignment with current FDA guidance on software and cybersecurity
- Responses to FDA and notified body questions
Compliance-Engineering für medizinische Geräte
Medical device compliance is where most programs quietly lose months, usually because design controls were treated as paperwork to catch up on later. We run the quality system as part of the build instead, so traceability between applicable user needs, design inputs, design outputs, risk controls and verification or validation evidence is maintained as the product evolves.
- Design controls and design history file setup
- IEC 62304 software lifecycle at your device safety class
- ISO 14971 risk management and hazard analysis
- Traceability matrices from requirement through to test
- Computerized system validation and electronic records controls under 21 CFR Part 11, where applicable
- CAPA and change control workflows your team can actually follow
Datenschutz und Sicherheitsstandards im Gesundheitswesen
Healthcare data compliance starts with knowing where protected health information really travels, which is rarely what the architecture diagram shows. We map the live flows first, then design access control and encryption around them so the obligations that come with it are enforced by the system rather than by a policy document nobody reads.
- HIPAA compliance risk assessments under the Security and Privacy Rules
- GDPR and ISO 27701 alignment for EU patient data
- SOC 2 Type II and HITRUST readiness programs
- Access control, audit logging, encryption, and key management
- Business associate agreements and vendor risk review
- Incident response and breach notification procedures
Cybersicherheit von angeschlossenen Geräten und die Einhaltung der Vorschriften nach der Markteinführung
A connected device carries compliance obligations long after it ships. Under Section 524B, the FDA expects a cybersecurity plan and a software bill of materials with the submission, and it expects you to keep patching once the fleet is in the field. We build the update path that makes those commitments safe to keep.
- Premarket cybersecurity package under FDA Section 524B
- Software bill of materials generation and ongoing maintenance
- Threat modeling and penetration testing for connected devices
- Signed over-the-air updates with tested rollback
- Vulnerability monitoring and coordinated disclosure
- Post-market surveillance and adverse event reporting workflows
Compliance mit Medicare- und Medicaid-Erstattung
Getting paid has a rulebook of its own. We help digital health platforms and healthcare organizations operate inside CMS requirements without redesigning the product every time a reporting rule shifts underneath them.
- CMS program eligibility and enrollment requirements
- Coding and claims rule alignment
- Quality reporting and data submission workflows
- Recordkeeping standards that survive a payer review
- Controls against fraud, waste, abuse, and improper payments
Compliance im klinischen Labor
Laboratory software carries the weight of the result it reports. We help diagnostic platforms and laboratory information systems meet CLIA requirements in the way the workflow actually runs, so compliance holds up on a busy day rather than only on paper.
- CLIA workflow and data handling review
- Result reporting and record retention design
- Instrument and LIS integration under CLIA constraints
- Validation protocols and inspection readiness
- GLP alignment for research environments
Einhaltung der Langzeit- und postakuten Betreuungspflichten
Post-acute care runs under rules the rest of healthcare rarely meets, and the software has to keep up with all of them. We build services to help home health and hospice agencies handle electronic visit verification and care documentation, without turning every shift into data entry.
- Electronic visit verification implementation
- Care records and retention rules
- State-level Medicaid program variation
- Patient data privacy in home and community settings
- Billing workflows for hospice and home health
Entdecken Sie unsere Fälle
Standards and regulations we work to
Which of these apply depends on what you build and whose patient data passes through it, so here are the two sets our teams work on most often.
Medical device compliance standards
Medical device compliance is everything a device and its software have to satisfy before and after they reach the market, from the quality system and the software lifecycle to the documented evidence that all of it was followed.
ISO 13485
Quality management system for medical devices, including design controls and supplier management.
21 CFR Part 820 (QMSR)
US quality system requirements, which now incorporate ISO 13485:2016 by reference.
IEC 62304
Software lifecycle processes, scaled to safety class A, B, or C.
ISO 14971
Risk management across the full product lifecycle, including post-market data.
EU-MDR 2017/745
Technical file, clinical evaluation, and post-market surveillance for the EU.
FDA Section 524B
Cybersecurity plan, patchability, and a software bill of materials at submission.
Patient data and care operations standards text section
For a hospital or a home health agency, the weight sits in how patient information is handled rather than in a product submission.
HIPAA Security Rule
Safeguards for electronic protected health information, from access control through to encryption.
HIPAA Privacy Rule, HITECH
How patient information may be used and disclosed, plus breach notification duties.
DSGVO
Lawful basis and data subject rights for EU patient data, including cross-border transfers.
SOC 2 Type II, HITRUST CSF
Independently attested security controls, asked for in enterprise procurement rather than by law.
CLIA
Quality and reporting requirements for diagnostic testing and the systems supporting it.
CMS conditions of participation
Program rules for Medicare and Medicaid participation, including electronic visit verification.
Gesundheitsrechtliche Herausforderungen, die wir lösen
Programs that reach us mid-flight tend to arrive with a version of the same few problems, so here is how each one gets handled.
Geben Sie Kliniker Daten, auf die sie noch am selben Tag reagieren können
Every problem in this table is cheaper to catch at the design stage. That is the case Simon Jones makes in his session, and he goes further into the timing than we can here.
Сompliance success stories
Programs where our medical device regulatory compliance services ran alongside the engineering, and what that produced.
Сompliance solutions we deliver
Some teams come to us with a product already in the market and a finding to close, others while they are still deciding which pathway to take.

Connected medical devices and IoMT
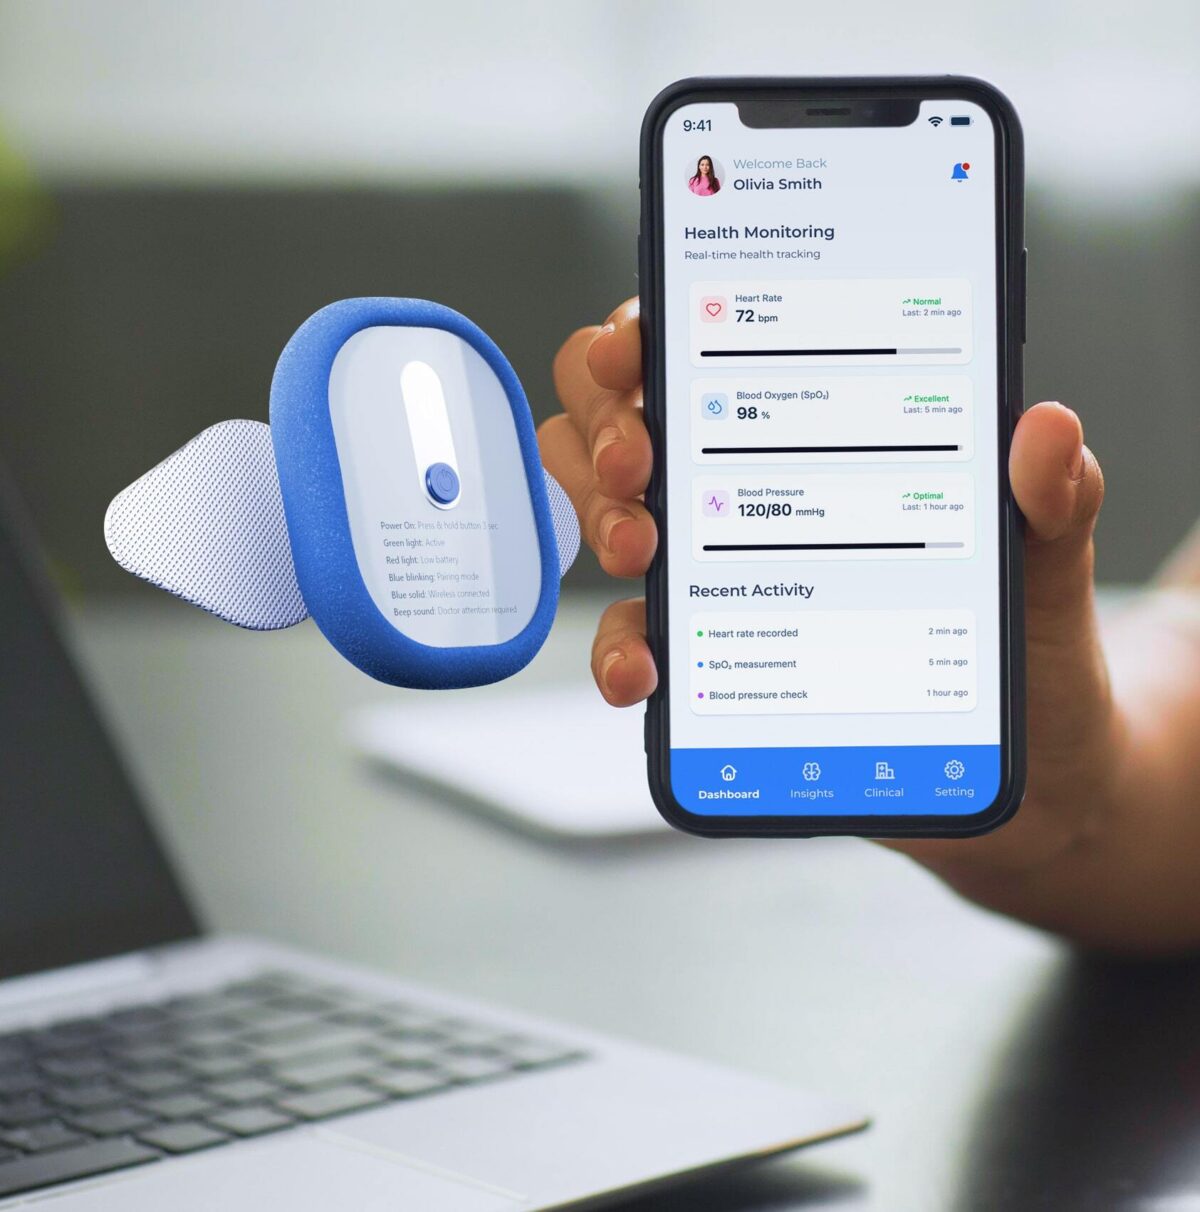
Wearables and bedside devices, from the firmware up to the cloud service behind them, built to the cybersecurity expectations that now come with a submission.
Software as a medical device
SaMD platforms developed under IEC 62304, with the risk file and the validation evidence a reviewer will ask to see.
EHR and EMR interoperability
FHIR and HL7 integrations with hospital systems such as Epic and Cerner, scoped so shared data stays inside its privacy boundary.
Secure cloud migration
On-premise workloads moved to AWS or Azure with the controls HITRUST and SOC 2 require, and nothing left behind on the old servers.
Clinical trial and laboratory platforms
Systems for decentralized trials and diagnostics, aligned to GxP expectations and validated under 21 CFR Part 11.
AI in clinical software
Governance and oversight for clinical software that uses artificial intelligence, including predetermined change control plans and the evidence the EU AI Act is bringing in.
Fahrplan zur Einhaltung der Gesundheitsvorschriften
Every stage produces something you could hand to a reviewer, so progress stays visible while the work is still underway.
Requirements discovery and gap analysis
We start by assessing your architecture and the processes around it against the frameworks you have to meet. You get a remediation plan with the critical risks ranked first and a straight read on how much engineering each one takes.
Risk assessment and architecture design
For medical device scope, we perform ISO 14971 risk management activities. In parallel, privacy and security risks are assessed using the applicable security and privacy frameworks, and the resulting technical controls are incorporated into the architecture.
Implementation and remediation
Right after that, our engineers implement the remediation while bringing the software lifecycle, documentation and engineering controls into alignment with IEC 62304 where applicable, then configure the cloud environment against HITRUST controls. This is the part most consultancies hand back to you.
Validation and evidence
Then comes validation. We execute the verification and validation activities required by the applicable quality system and regulatory framework, and compile the resulting evidence into the design and development file or EU technical documentation.. Because the traceability was there from the start, this stage assembles evidence instead of hunting for it.
Audit support and maintenance
Finally, our compliance professionals sit with you through an FDA inspection or a SOC 2 audit and answer the questions in the language they use. After launch, we help you maintain compliance as the regulatory environment moves, which right now mostly means device cybersecurity and AI governance.
Wo steht Ihr Programm?
Tell us what you are building or operating and what already exists. We map what is missing and the team shape it takes to close it.
Frameworks und Technologien, mit denen wir arbeiten
Which of these applies depends on your product and your markets, so here is what our compliance and engineering teams work with most often.
ISO 13485
IEC 62304
ISO 14971
IEC 62366-1
21 CFR Part 820 (QMSR)
21 CFR Part 11
EU-MDR 2017/745
GAMP 5
IEC 60601-1
UKCA
HIPAA
HITECH
DSGVO
SOC 2 Typ II
HITRUST CSF
ISO 27001
ISO 27701
NIST CSF
FDA Section 524B
SBOM (SPDX, CycloneDX)
HL7 FHIR R4
HL7 v2
DICOM
SMART auf FHIR
USCDI
IHE profiles
OMOP CDM
Rust
C and C++
Python
Eingebettetes Linux
AWS Control Tower
Azure-Richtlinien
Terraform
Kubernetes
HashiCorp Vault
Jira and Confluence
GitHub and GitLab
DocuSign
Haben Sie Probleme mit den FDA- und ISO-Anforderungen?
Download our guide to ISO 13485 and FDA compliance for faster medical device development. It covers the certification path stage by stage and the mistakes that most often stall a device before it reaches review.
Why teams choose Yalantis for healthcare compliance consulting
Engineering-First-Compliance
We are one of the few firms in this market that can build what we recommend. The finding and the fix come from the same organization, so a finding turns into merged code rather than into a second procurement cycle.
A certified quality system you inherit
Our internal quality management system is certified to ISO 13485 and ISO 9001, and your project runs inside it. That means controlled documents and traceable decisions from day one, which usually saves your organization’s quality team a supplier qualification round.
Firmware to cloud under one roof
A connected device usually fails at the seams between layers. We cover the whole path from embedded firmware to the cloud platform behind it, so those seams are ours to answer for.
Rust, bei dem ein Speicherfehler einen Rückruf bedeuten würde
We use memory-safe languages for critical firmware, which removes an entire class of memory bug before it can turn into a safety incident or a field action. Our C and C++ depth stays in place for the code you already own.
Global market access
Whether you are entering the US under the FDA or Europe under MDR and GDPR, we know where the requirements diverge and where one set of evidence can serve several markets. UKCA marking for the UK usually rests on the same foundation.
Compliance that runs in your pipeline
Automated tests and generated records live in your CI/CD process, so you stay ready for a review instead of preparing for one. Your quality team spends its time on judgment calls instead of assembling spreadsheets before a review.
Certifications we hold
Your project runs inside our own certified quality system, so the controls reviewed in our own certification cover the work we do for you.
ISO 13485
Medical device quality system
ISO 9001
Qualitätsmanagement
ISO 27001
Informationssicherheit
Referenzen
Erfahrungen aus der Bereichsgestaltung für tragbare Geräte und das Internet der Dinge
Artikel
Wofür wird Rust verwendet? Ein Leitfaden für reale Anwendungsfälle im Jahr 2026
Erfahren Sie, warum Rust so beliebt ist, wie Ihr Unternehmen von der Einführung profitieren kann und wie die Marktaussichten für diese Sprache sind, um zu lernen, wie man Rust-Entwickler findet.
Artikel
Wie man Firmware-Schwachstellen mit Secure Boot und OTA-Updates verhindert
Entdecken Sie, wie Sie Firmware-Schwachstellen verhindern und vernetzte Geräte im großen Maßstab sicher, konform und wiederherstellbar halten.
Artikel
KI in der Produktentwicklung: Wie man manuelle Arbeit automatisiert und den PDLC beschleunigt
Entdecken Sie das KI-gestützte Framework für den Produktentwicklungslebenszyklus, das von Yalantis entwickelt wurde
Let’s map your path to compliance
Tell us what you are building or operating, and which rules you have to meet. Our compliance lead comes back with what we can already see and a compliance plan for closing it, plus the two or three questions worth answering before anything starts.
Artikel
Wie vernetzte Gesundheitsgeräte die Versorgung verändern und das Marktwachstum antreiben
Erfahren Sie, was vernetzte Gesundheitsversorgung ist, worin ihr grundlegender Unterschied zur Telemedizin besteht, welche Geschäftschancen sie eröffnet und was für die Entwicklung eines vernetzten Medizinprodukts erforderlich ist.

Artikel
HIPAA-Konformität für Softwareentwicklung: Checkliste und Anforderungen
Dieser Leitfaden enthält umfassende Informationen dazu, wie Sie die Einhaltung der HIPAA-Vorschriften sicherstellen können. Außerdem erfahren Sie, wie Sie Sicherheitsmaßnahmen umsetzen, um die Anforderungen der HIPAA-Sicherheitsvorschrift zu erfüllen.
Artikel
Rust für Medizingeräte: Zertifizierte Software für sicherheitskritische Systeme
Erforschen Sie, wie Rust die Software von Medizinprodukten durch Speichersicherheit, Leistung und Zuverlässigkeit verbessern kann und Entwicklern hilft, sichere und zuverlässige eingebettete Systeme zu entwickeln.
Verwandte Dienstleistungen und Branchen
FAQ
-
Was sind Gesundheitsdienstleistungscompliance-Services und was beinhaltet sie?
Sie umfassen die Arbeit, um ein Produkt an die geltenden Vorschriften anzupassen: die Datenschutzbestimmungen unter HIPAA oder GDPR für Patientendaten und die Regeln für Medizinprodukte unter der FDA oder der EU MDR, sobald Ihre Software einen klinischen Zweck erfüllt. Ein vollständiges Compliance-Programm für die Gesundheitsbranche erstreckt sich von der ersten Bewertung über das Risikobuch und die technischen Kontrollen bis hin zum Nachweispaket, das dahinter steht. Beratungsleistungen beschränken sich in der Regel auf die Empfehlung, und wir übernehmen die Umsetzung, sodass die Compliance-Experten, die ein Problem feststellen, mit den Ingenieuren zusammenarbeiten, die das Problem beheben.
-
Welche Vorschriften und Normen gelten für die Gesundheitssoftware?
Which compliance requirements apply depends on what the software does. If it stores or transmits protected health information in the US, HIPAA and HITECH apply, and anything touching EU residents brings in GDPR. If the software has a medical purpose, it becomes a device, and then you are looking at 21 CFR Part 820 under the QMSR and IEC 62304 for the software lifecycle, with ISO 14971 governing risk management throughout.
Selling in Europe adds the EU MDR. Enterprise buyers usually ask for SOC 2 Type II or HITRUST as well, though neither is a legal requirement, and both tend to show up in procurement long before a contract does.
-
Was ist die Konformität von Medizinprodukten und wie unterscheidet sie sich von den allgemeinen Regeln im Gesundheitswesen?
Die Einhaltung der medizinischen Gerätevorschriften ist die engere der beiden Kategorien. Sie umfasst die Anforderungen, die eine regulierte Medizin-Einrichtung und ihre Software erfüllen müssen: ein Qualitätsmanagementsystem nach ISO 13485 und ein Software-Lebenszyklus nach IEC 62304, mit einem aktuellen Risikobuch nach ISO 14971. Die breitere Kategorie umfasst Datenschutz- und Rückerstattungsbestimmungen sowie Pflichten, die für Organisationen in der gesamten Gesundheitsbranche gelten, wenn kein Gerät beteiligt ist. Viele Produkte fallen sowohl in diese als auch in die andere Kategorie, weshalb wir die regulatorischen und Einhaltungsarbeiten als ein Programm anstatt als zwei separate Programme abdecken.
-
Wie lässt man eine Medizinprodukte sicherheitshalber bei der FDA registrieren?
Start with classification, because the class decides your pathway and the evidence you have to produce. After that the work splits in two: a quality system that meets Part 820 as it now stands under the QMSR, and design and development controls that maintain traceability between applicable user needs, design inputs, outputs, risk controls and verification and validation evidence.
Software adds IEC 62304 documentation at whatever safety class your hazard analysis lands on, and a connected device adds a cybersecurity plan with a software bill of materials under Section 524B. Miss those and the submission can be refused before anyone reads the clinical content. The submission itself is mostly an assembly job, which is far easier when the evidence was produced as the product was built.
-
Was bedeutet die HIPAA-Compliance für Healthcare-Software und wem ist sie vonnöten?
HIPAA applies to covered entities such as providers and health plans, and to the business associates handling protected health information for them. Most health tech vendors are business associates, which means the Security Rule lands on you directly and a signed business associate agreement becomes a condition of doing business.
For a software team, healthcare software compliance comes down to access control, audit logging, encryption in transit and at rest, and a risk analysis you can produce on request. Policies and procedures are part of it, though the Security Rule also expects technical controls that enforce them. The risk analysis is what catches people out, because it has to describe the system as it runs today.
-
Kann Yalantis unsere Geräte zertifizieren oder das Zertifikat ausstellen?
Nein, und das ist wichtig zu klären. Zertifikate werden von einer Notifizierungsstelle oder einem akkreditierten Prüfer ausgestellt, und die Marktzulassung erfolgt über die FDA. Was wir tun können, ist die Zusammenstellung der Unterlagen zu optimieren und sicherzustellen, dass das Produkt, das dahintersteht, wie in der Dokumentation beschrieben funktioniert. Unsere eigene ISO 13485-Zertifizierung hilft Ihnen dabei, da Ihr Projekt innerhalb eines Qualitätsmanagementsystems abläuft, das bereits zertifiziert ist.
-
Wie lange dauert es, bis ein Gesundheitsprodukt auditbereit ist?
Bei einem bereits auf dem Markt erhältlichen Produkt mit einer Codebasis in einem vernünftigen Zustand dauert ein Programm zur Einhaltung der Datenschutzbestimmungen oder des SOC 2-Standards in der Regel drei bis sechs Monate, wobei der Großteil der Arbeit eher der Engineeringphase als der eigentlichen Programmierung zugeordnet ist. Ein erster Antrag bei der FDA für Software der Klasse II ist eine längere Strecke: In der Regel dauert es neun bis achtzehn Monate, nachdem das Projekt gestartet wurde. Was die Zahl an Zielen erreicht, bestimmt die Menge der Änderungen an der Architektur, um die Kontrollen zu unterstützen. Daher geben wir Ihnen nach der Bewertung ein Datum an, anstatt es vor der Bewertung zu nennen.
-
Wie stellen Sie sicher, dass ein angeschlossenes Medizintechnikgerät nach der Inbetriebnahme weiterhin funktioniert?
Post-market obligations never really stop. You have to watch every component in your software bill of materials for newly disclosed flaws and patch the ones that matter, then report events that cross the reporting threshold in each market you sell into.
All of that depends on patching being safe, so we set the update path up properly: signed images on A/B partitions, with a health check before the switch and a rollback tested on production hardware. Signing keys live in a hardware root of trust rather than a config file. Surveillance data then goes back into the risk file, which keeps your documentation current instead of frozen on the date of approval.
-
Kann ein Partner sowohl die Compliance-Arbeit als auch die technische Umsetzung übernehmen?
Yes, and that is usually why teams call us. Our medical device compliance consulting services sit in the same company as the engineers who write the firmware and build the cloud platform behind it, so a finding turns into a ticket rather than a report someone has to translate for a separate development vendor.
You can also take a single piece. Some teams bring us in for the assessment and nothing else, others for the IEC 62304 documentation on software that already exists, and we customize the scope from there.
-
Brauchen Gesundheitsstart-ups einen Compliance-Beauftragten oder kann das Outsourcing erfolgen?
In den Anfangsjahren outsourcen die meisten finanzierten Teams diese Aufgabe. Ein Teilbereichs-Compliance-Manager bietet Ihnen Compliance-Expertise, die bereits bei der Übermittlung und Inspektion eingesetzt wurde – ohne die Kosten einer festangestellten Position – und die Sie normalerweise durch die Einrichtung des Qualitätsmanagementsystems und die erste Übermittlung führt. Der Zeitpunkt, in dem diese Aufgabe intern durchgeführt wird, tritt in der Regel erst dann ein, wenn das Produkt auf den Markt gekommen ist und die Nachmarkttransparenz für ein internes Compliance-Team zu einer festen Aufgabe wird. Wir üben diese Aufgabe dann oft selbst aus und bleiben anschließend für die technische Umsetzung verantwortlich.
-
How much does medical device compliance work cost?
It follows the shape of the engagement. A gap analysis is a fixed scope that lands in weeks, while a remediation program is priced by the team it takes and how long the runway is. As a nearshore partner, our blended rate sits well below what large advisory firms charge, and a much bigger share of the budget goes into implementation instead of reporting, which makes a full remediation program more cost-effective than an advisory engagement of the same size. We put a number on it once that is done, since it depends on how much evidence already exists.
Erste Schritte mit Yalantis
Hinterlassen Sie Ihre Daten und ein paar Worte zum Projekt. Wir werden es prüfen und uns melden, um einen Termin zu vereinbaren.
Willkommen bei Yalantis. Bitte füllen Sie das Formular aus, wir melden uns dann bei Ihnen.
Vielen Dank, dass Sie uns kontaktiert haben.
Behalten Sie Ihren Posteingang im Auge. Wir werden uns in Kürze bei Ihnen melden. In der Zwischenzeit können Sie sich unsere besten Fallstudien ansehen und Kundenfeedback auf https://clutch.co/profile/yalantisu0022 target=u0022_blanku0022 rel=u0022noopeneru0022u003eClutch.u003c/au003eu003c/pu003e lesen.